
The governance layer for enterprise AI agents
Discover, identify, govern and audit every AI agent in your organization. No content decryption. No MITM certificates.

Overview
Verdicts follow the policies set in the GABA console.
The way we work is changing.AI agents write code, read files and run commands.Rutile makes every one of those actions visible and controllable.So enterprises can use AI more boldly, instead of blocking it.
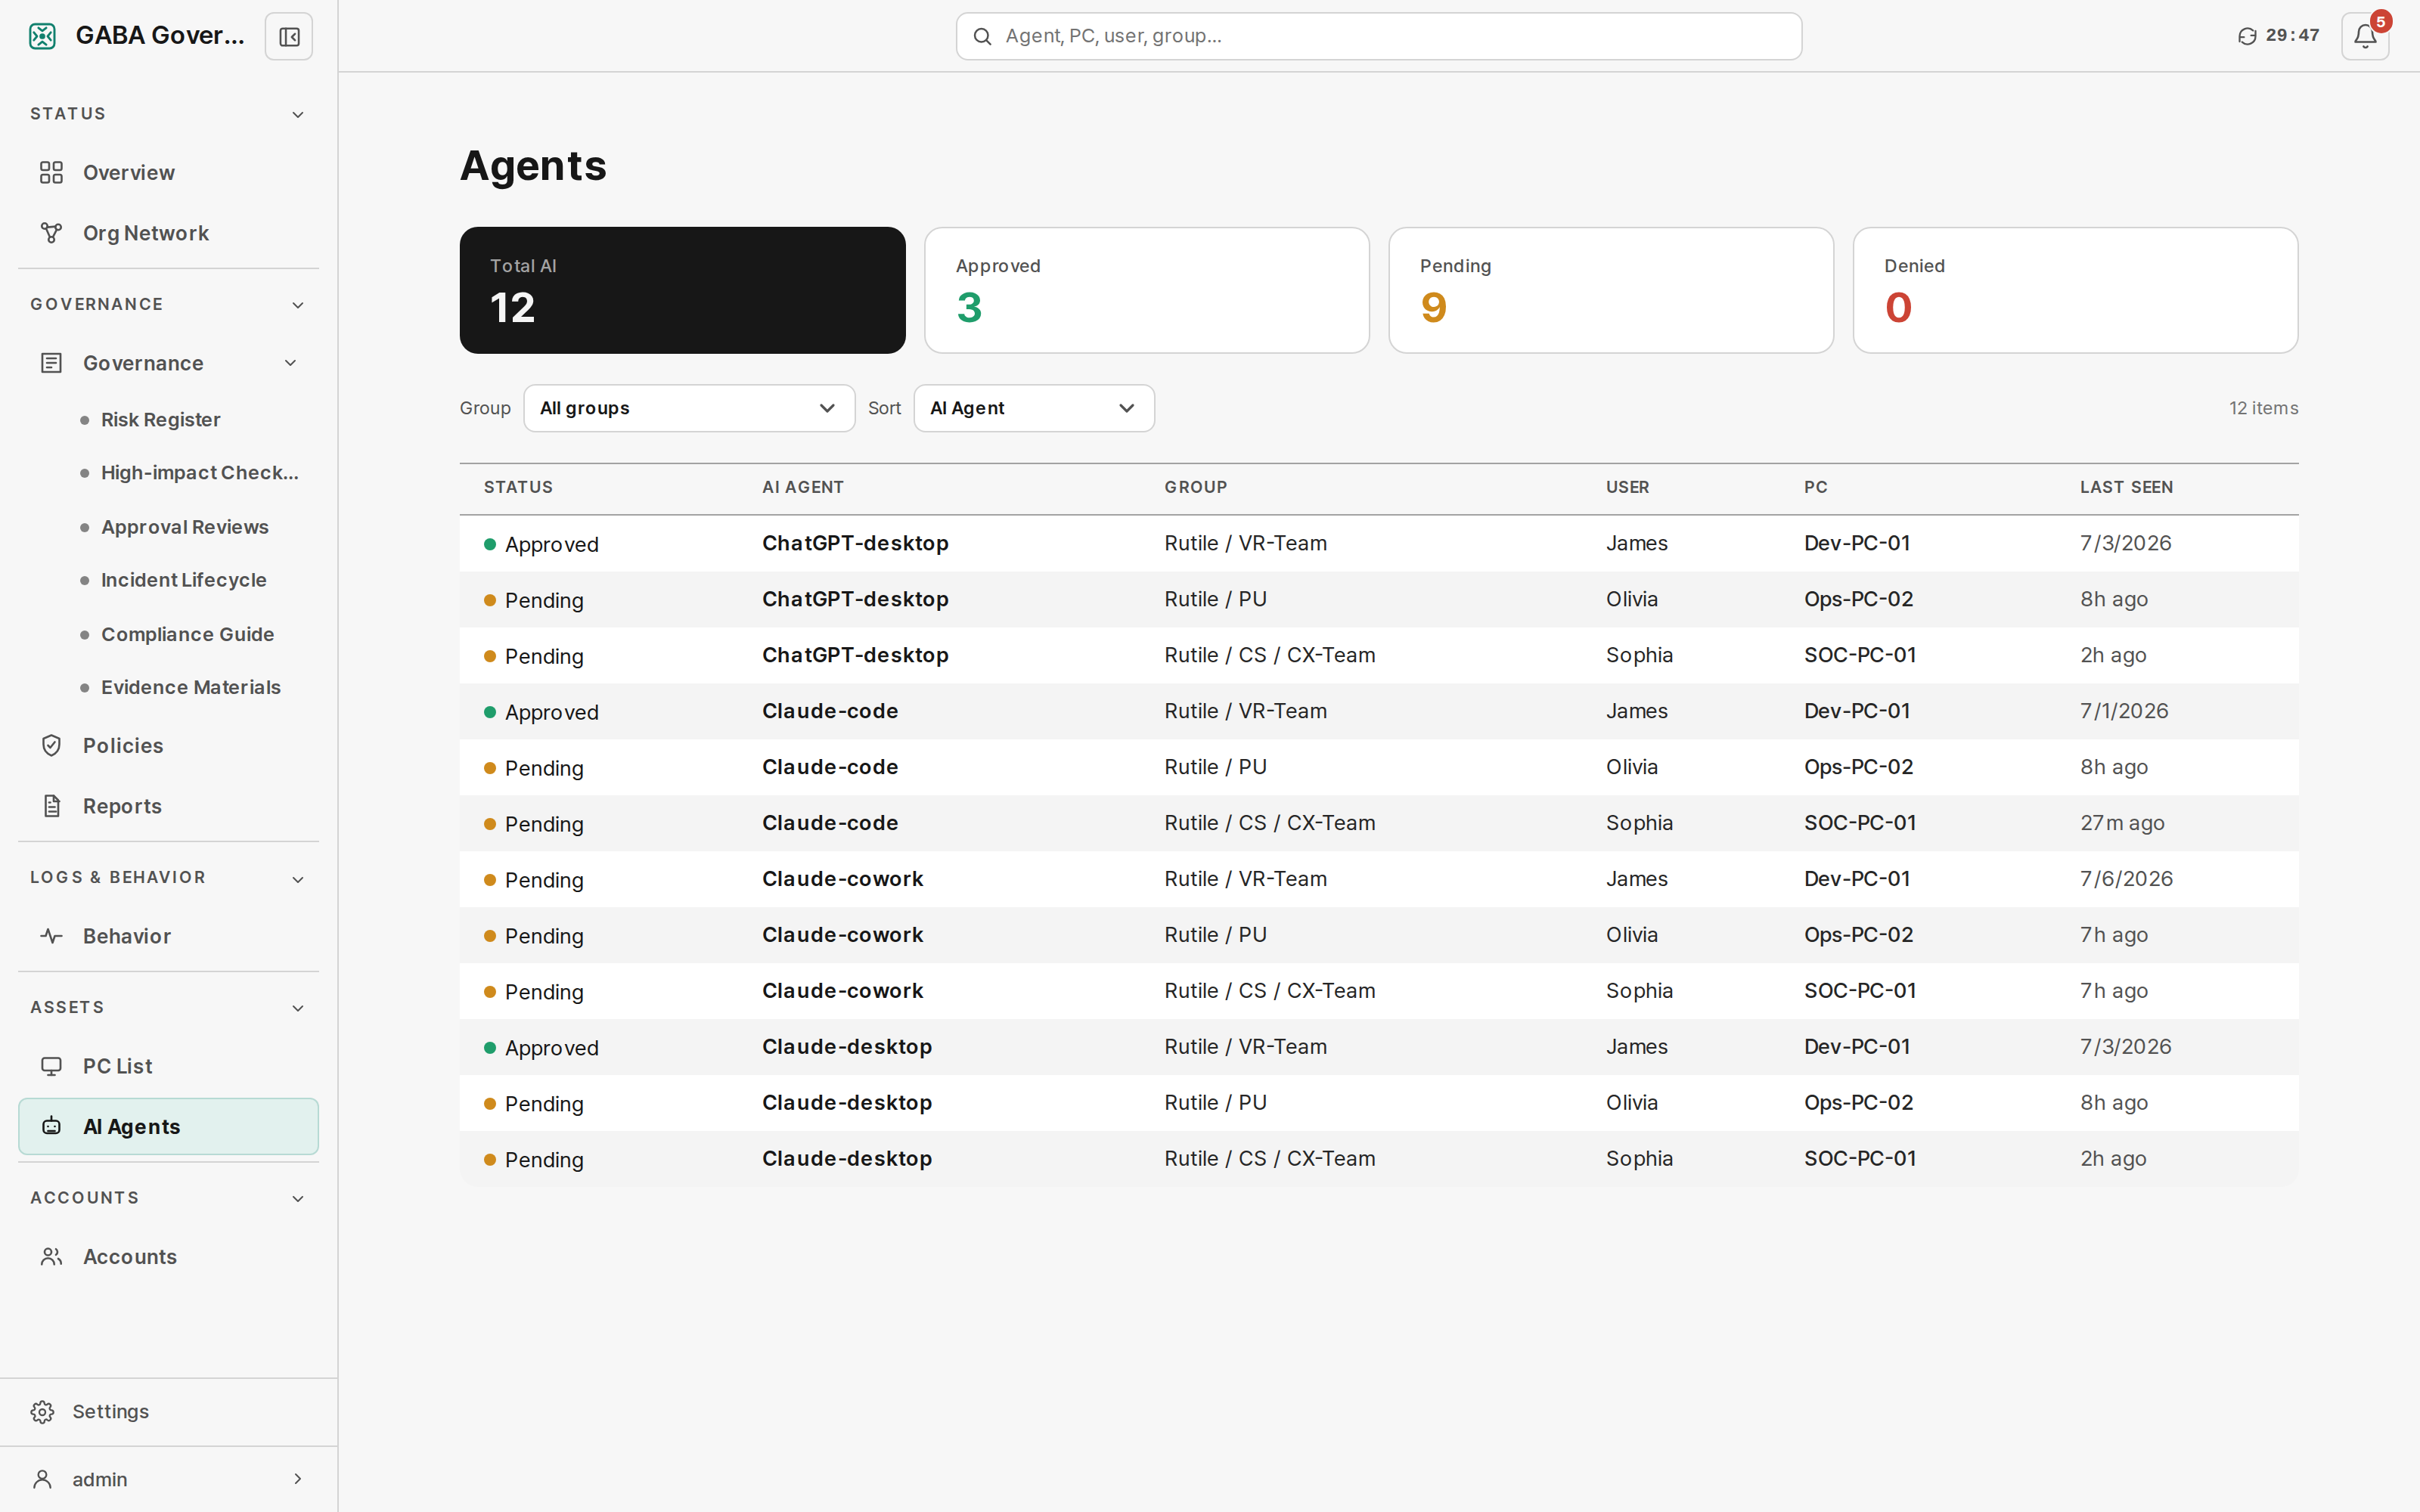
Every AI tool, visible within a second
An endpoint agent detects AI tools instantly from OS kernel signals and assigns a persistent identity (DID) from independent evidence layers. Identity survives tool updates.
- No opt-in required, automatic detection
- Identified by binary signature and process context
- Tampering (signer swap) flagged instantly
Policy on behavior, not vendors
"Blocked the instant a secret file is read." The same action gets the same rule, whatever the AI tool. Decisions and enforcement run on the endpoint and finish within 100ms.
- New AI tools need no new rules
- Local defense holds even if the server is down
- Approval workflow for exceptions
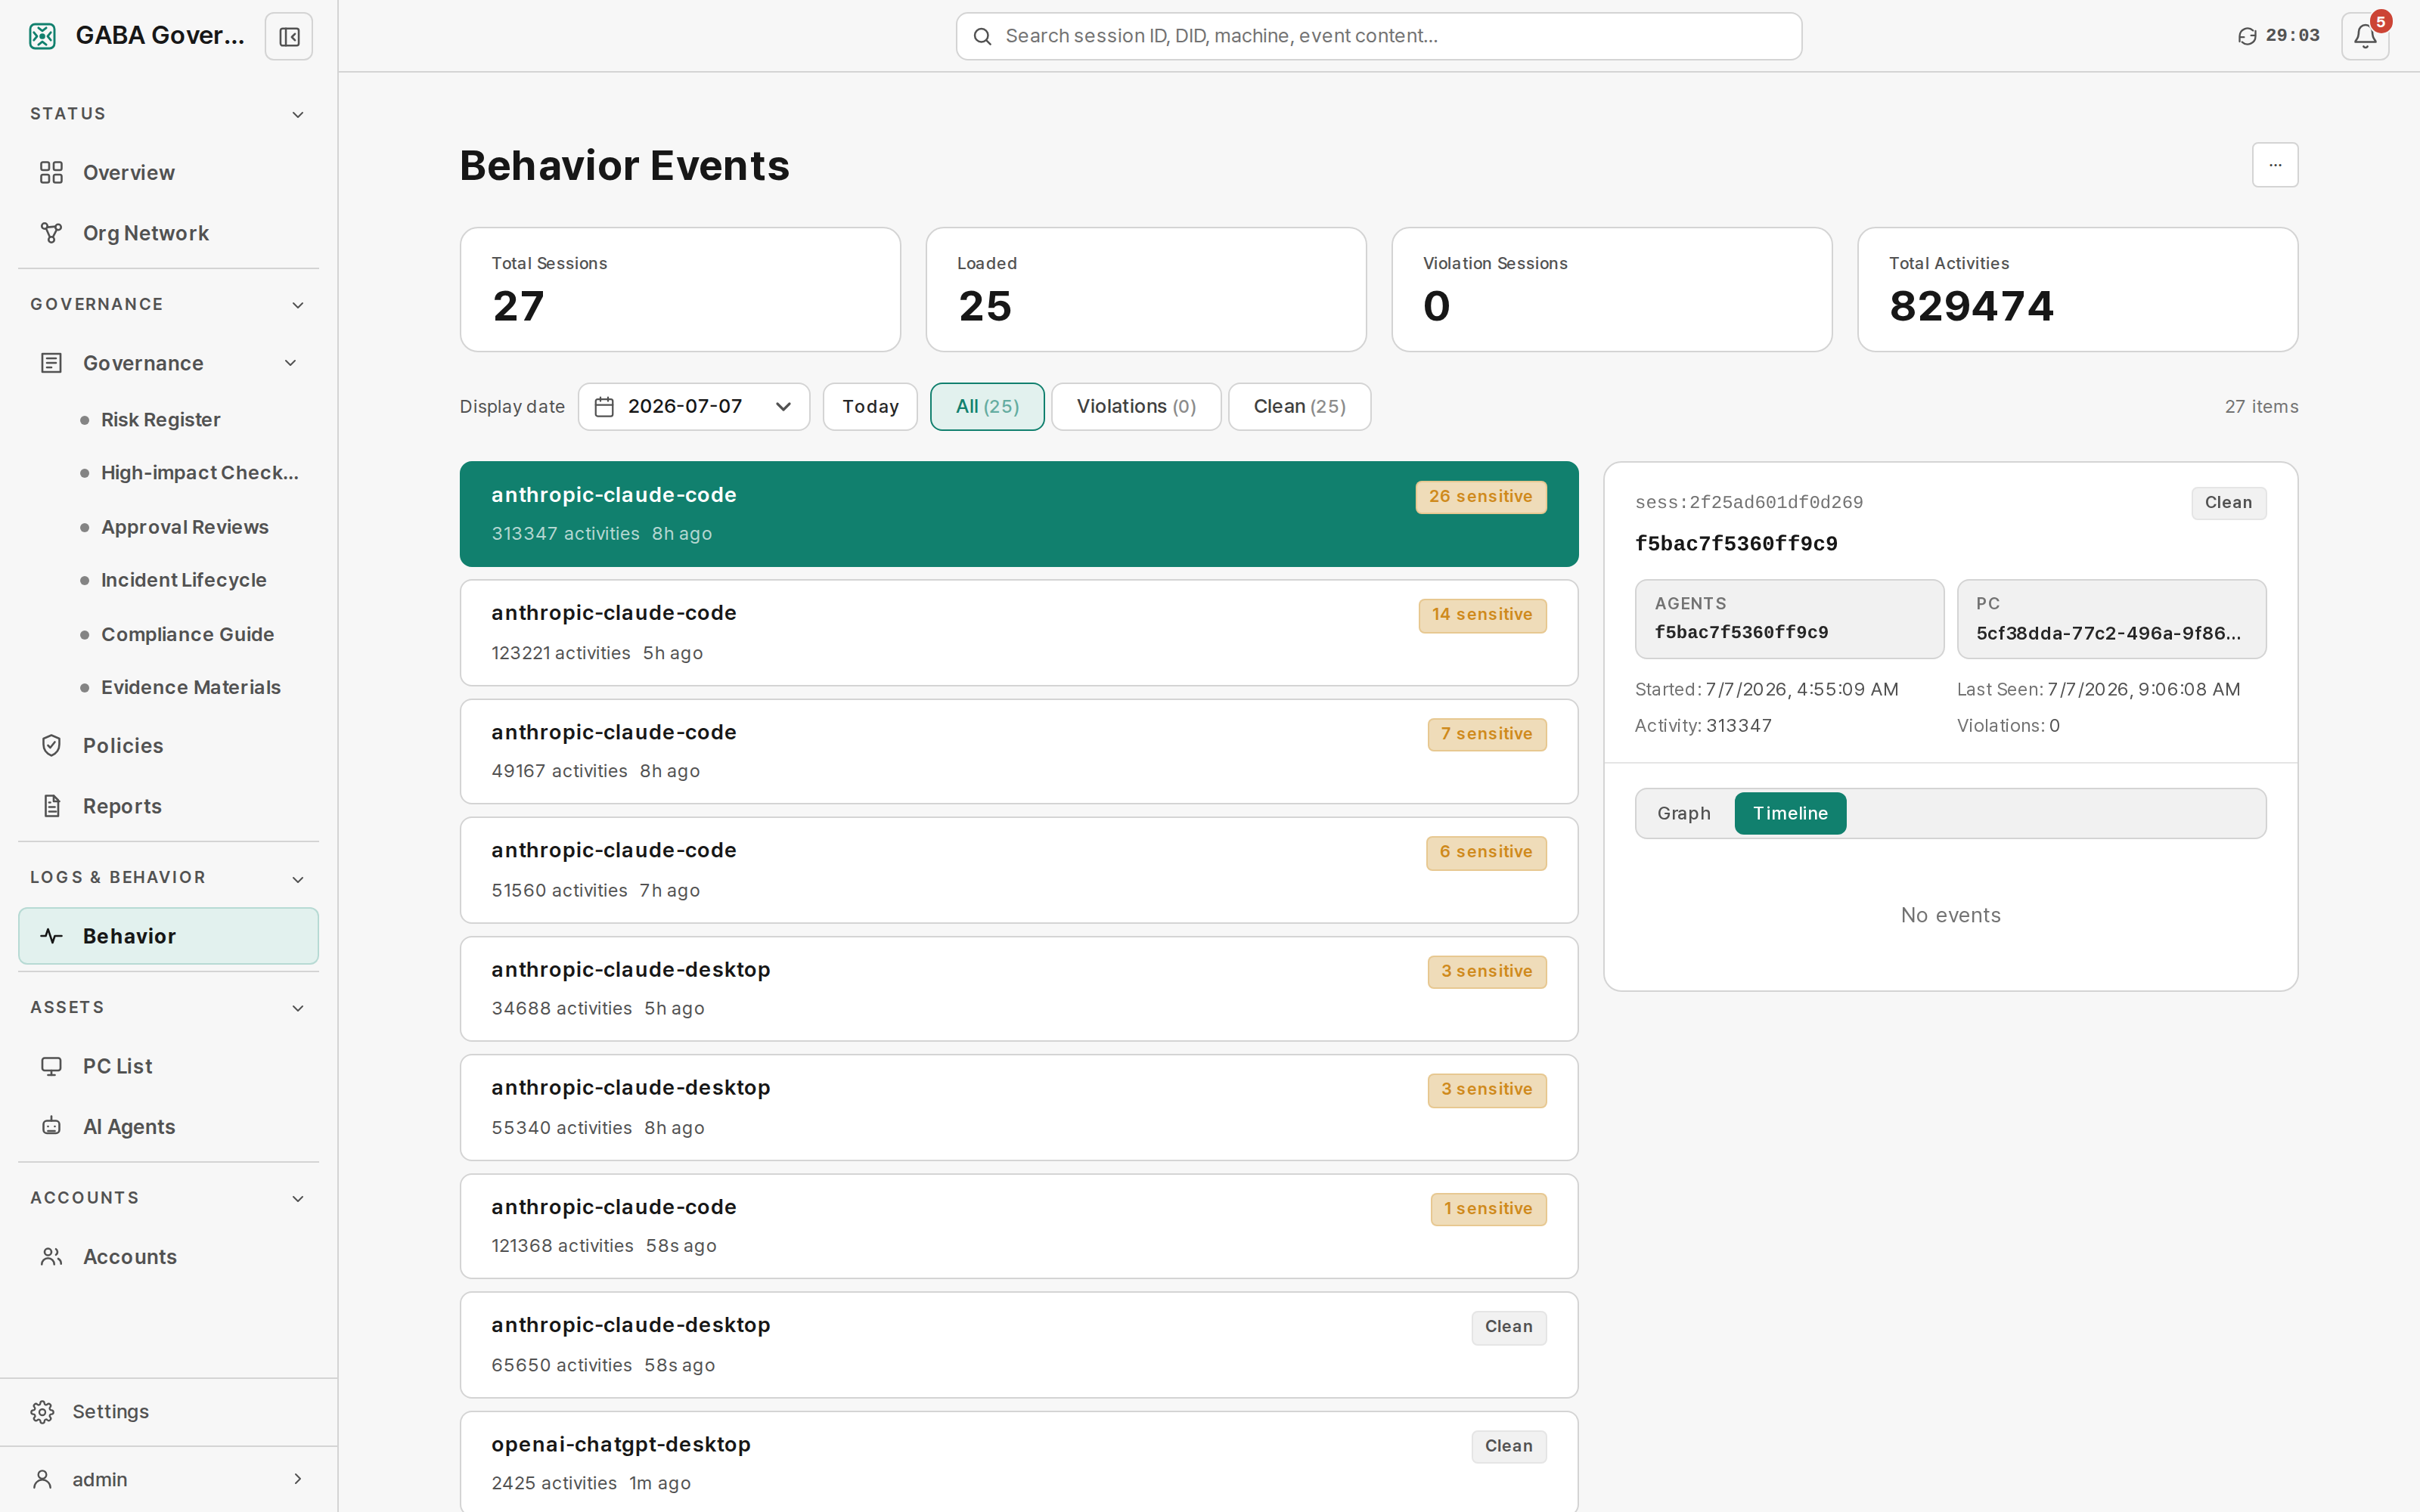
Every decision, sealed immutably
Who, when, what: every policy decision and its evidence is sealed into the log. Built to meet the audit-trail requirements of ISMS-P and financial supervisory regulation.
- Compliance built on the EU AI Act and OWASP LLM Top 10
- Matched evidence and approver recorded
- Searchable audit console
HOW GABA WORKS
From the agent to the dashboard
Receives the policy bundle
Reads a file /
calls a tool Instant allow/
block by local policy Sends activity /
tool_call / decision events Stores logs and shows behavior events
Go deeper
Product, how it works, security, demo. Jump straight to the page you need.
Companies building with us
People building with us


Don't block AI. Make it controllable.
See how GABA Governance works in a 30-minute demo.